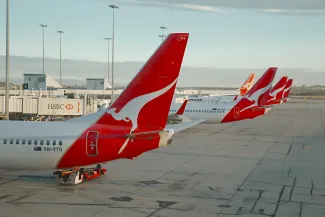
Stay current with our airline news coverage.
The breach at a glance
According to a press summary of Qantas’ internal findings shared with multiple outlets, a July intrusion on a third-party platform exposed more than 1,000,000 customers’ sensitive details—including phone numbers, birth dates and home addresses—while another 4,000,000 customers lost the privacy of their name and e-mail address. The files resurfaced on illicit forums last week after the hacker collective known as Scattered Lapsus$ Hunters published the cache when a ransom deadline passed, the Guardian Australia reported. In a prepared statement, the airline said it is working “with the help of specialist cyber security experts … to investigate what data was part of the release.” Qantas has also obtained an injunction intended “to prevent the stolen data being accessed, viewed, released, used, transmitted or published by anyone, including third parties.”Why this matters for travelers
Qantas is Australia’s flag carrier, and its frequent flyer program is a passport to upgrades, partner airlines and hotel perks across the globe. If you have used the airline’s websites, mobile app or loyalty portals in recent years, the compromised data points could be enough for criminals to:- Reset account passwords and siphon hard-earned points.
- Launch phishing emails that appear to come from Qantas or trusted partners.
- Triangulate personal details for broader identity-theft schemes, including passport or driver’s-license fraud.
Timeline: from July hack to October data dump
- Early July: Attackers infiltrate a third-party platform used by Qantas, extracting multiple customer databases.
- July disclosure: Qantas publicly confirms the breach, noting that millions of records were stolen.
- Ransom demand: Scattered Lapsus$ Hunters give the airline a deadline to pay for the data’s return.
- Sunday, Oct. 12: After the deadline expires, the hackers publish the full trove of files. Qantas issues an update and seeks legal protection to limit distribution.
How Qantas is responding
- Deploying external forensic teams to audit every database touched during the hack.
- Notifying customers whose passport, driver’s-license or Medicare details appear in the leaked set.
- Offering complimentary credit-monitoring services for those most at risk. The duration of coverage is still “[Not specified in release].”
- Enforcing forced password resets on Qantas.com and the Qantas App.
- Bolstering multifactor authentication across its digital touchpoints.
Travel-centric tips for safeguarding your data
1. Change passwords—everywhere you reused them
Even if your Qantas account already prompts a reset, swap out log-ins on any site where you recycled the same credentials.2. Enable multifactor authentication (MFA)
Apps like Google Authenticator or physical security keys add a hurdle that simple password theft cannot bypass.3. Watch for phishing that impersonates Qantas
Be suspicious of messages demanding urgent action, especially those linking to unfamiliar domains or asking for payment details.4. Freeze your credit file
A credit freeze blocks new credit lines until you personally unfreeze them—an effective shield against fraud.5. Check your loyalty balance regularly
Mileage fraud often starts with small, unnoticed redemptions; set alerts for any point activity.What other airlines—and travelers—can learn
The Qantas incident underscores an uncomfortable truth for the aviation sector: robust cockpit doors do nothing against digital break-ins. Airlines sit on vast repositories of personal data, from passport scans to payment cards and even meal preferences, making them a prime target. Industry analysts say the next wave of resilience will hinge on three pillars:Implementing zero-trust architectures that assume every user is a potential intruder, encrypting data at rest and in transit, and rigorously vetting third-party vendors.The Guardian noted that government-mandated cyber-resilience laws enacted after the 2022 Optus and Medibank attacks compel Australian companies to disclose breaches quickly and upgrade security controls, but execution remains uneven. For travelers, the best defense is opting into security features—whether that means MFA, biometric log-ins or point-redemption alerts—whenever they sign up for an airline or hotel program.
Frequently asked questions (FAQ)
- Is my passport number exposed?
- Qantas has not specified passport exposure rates publicly. Affected flyers will receive direct communication.
- Do I need a new Frequent Flyer number?
- No. Points accounts remain valid, though you should change associated passwords and enable MFA.
- Will the breach affect my upcoming flights?
- Flight bookings, boarding passes and airport operations are running normally. Check in as usual but monitor your e-mail for legitimate updates.
- How do I claim complimentary credit monitoring?
- The carrier will send instructions to qualified customers. If you believe your data is compromised and have not been contacted, reach out to Qantas customer care.
- Can I sue for damages?
- Australia’s Privacy Act allows for complaints to the Office of the Australian Information Commissioner. Consult a legal advisor to explore class-action options.
Looking ahead: travel after the Qantas data breach
In the hyperconnected world of loyalty apps and digital boarding passes, personal information has become its own form of currency—and vulnerability. While Qantas works to rebuild trust, the breach is a reminder that no itinerary is immune to cyber turbulence. For now, the smartest move is proactive housekeeping: update passwords, scrutinize statements, and think twice before clicking any link that claims to fix the problem for you. The airline may be grounded in legal remedies, but travelers hold the power to steer their own data-safety flight plan.— as Qantas outlined in a prepared statement.
Explore more Australia travel →
More travel news
Saudi Arabia: Australia Raises Advisory to Do Not Travel
Australians should postpone all Saudi Arabia trips, including religious travel; those already there should consider leaving if safe and confirm flights before going to an airport.
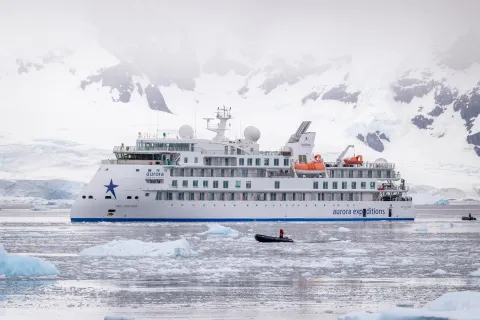
Aurora Expeditions Welcomes Kids on Remote Voyages
Sydney, Australia - Aurora Expeditions has lowered its minimum age requirement to six, bringing families with school-age children onto expedition ships bound for Antarctica, the Arctic and other remote regions.
Australia Replaces Paper Forms With Digital Travel Cards
Sydney, Australia - The Australian government announces nationwide rollout of digital passenger cards to eliminate paper forms at all international entry points over the next 12 to 18 months.
Discover the Deadly Beautiful Spots Behind Apex
SYDNEY, Australia - Baltasar Kormákur's survival thriller Apex turns New South Wales wilderness into cinema's latest adrenaline playground, with implications for set-jetting tourism and conservation access.
About the Author
Andy Wang
Andy Wang is Asia Editor at Jetsetter Guide, covering Southeast Asian travel and food from his base in Singapore. A first-generation American, he brings a dual perspective to the region.